AI Governance Layer for Financial Data
Letting banks and fintechs run AI models on customer data without ever exposing it. Powered by Trusted Execution Environments (TEE).
The Problem
Every institution wants AI on customer data. None of them are allowed to risk it.
How It Works
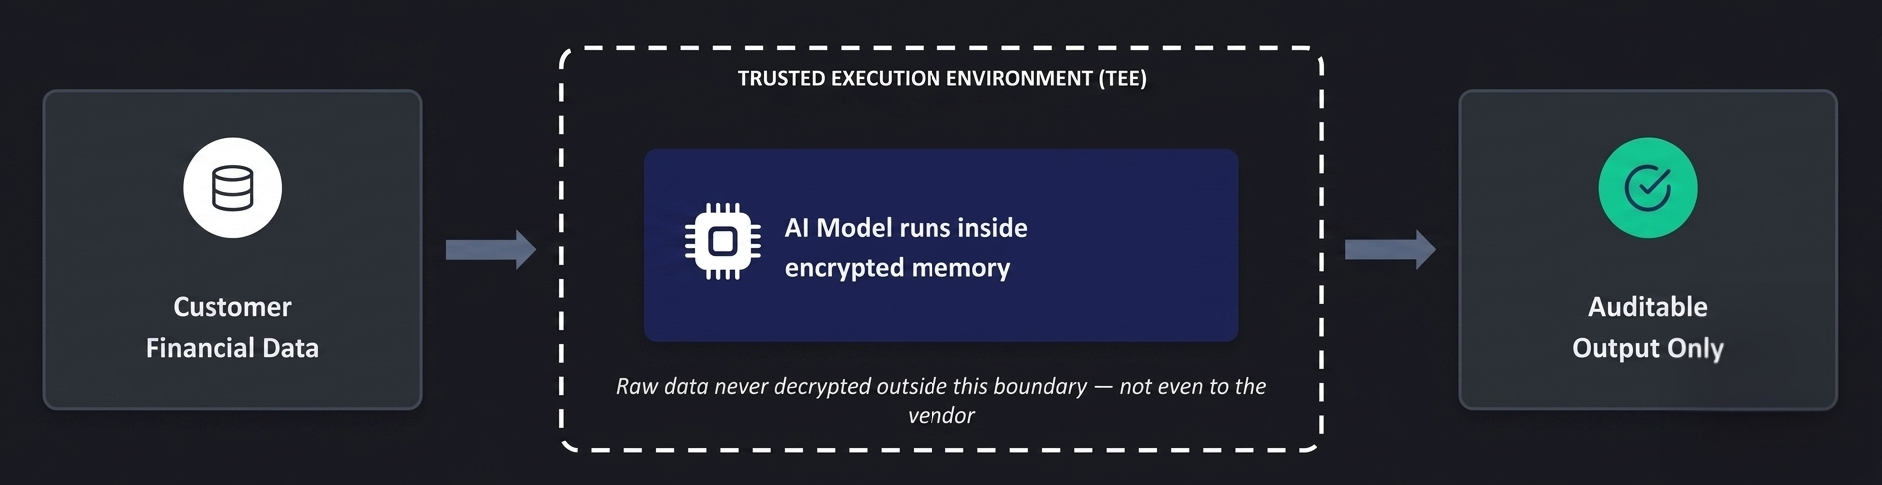
Governance by design: data and model, both inside the TEE
Encrypted customer data and the AI or risk model run together, encrypted, inside the enclave — producing a verified decision or score for the lender, regulator or auditor.
Under The Hood
From encrypted input to verified output, in five steps
Encrypt
Data & code encrypted at the source
Load
Moved into a hardware-isolated enclave (TEE)
Attest
Remote attestation verifies enclave integrity first
Compute
Runs on isolated memory — invisible to host OS/admin
Release
Only the approved output is decrypted & shared
Runs on silicon-level isolation: Intel SGX / TDX · AMD SEV-SNP · ARM CCA · NVIDIA Confidential Computing GPUs
Flexible By Design
One confidential compute layer, deployed however you need it
On Public Cloud
Run inside the confidential-computing offering of any major cloud
- Azure Confidential ComputingDCsv3/v5 VMs, confidential containers
- AWS Nitro EnclavesIsolated compute within EC2
- Google Confidential VMs / SpaceConfidential GKE & data clean rooms
On Your Own Hardware
Open-source frameworks, run in your own data centre
- Gramine / Open Enclave SDKRun unmodified apps inside an enclave
- EGo & EnarxDeveloper tooling for TEE application builds
- Full data sovereigntyOn-prem, air-gapped or private-cloud options
PryvX abstracts the hardware & cloud layer — same policies, same attestation, same guarantees, wherever you run it.
How It Compares
Confidential computing is one of several PETs — each with different tradeoffs
| Privacy Tech | What it protects | Performance | Best fit |
|---|---|---|---|
| TEE / Confidential Computing | Raw data — hardware-isolated | Near-native | General-purpose AI/ML on joint, sensitive data |
| Homomorphic Encryption (HE) | Data stays encrypted, always | Slow (heavy overhead) | High-value compute without hardware trust |
| Federated Learning (FL) | Raw data — stays on each party's infra | Fast, but network-bound | Joint model training without moving data |
| Differential Privacy (DP) | Individual records, via noise | Fast | Aggregate analytics, some accuracy loss OK |
| Secure Multi-Party Computation (MPC) | Inputs from distrustful parties | Moderate – slow | Joint computation with no single trusted party |
PryvX is built TEE-first — the only PET that runs full, unmodified AI models on raw sensitive data at near-native speed.
“How do I let my teams use LLMs on customer data without violating DPDP Act or RBI guidelines?”
TEE is the mechanism. Compliance-enabled AI adoption is the answer.